From Brno to Mainz
Jiří Brada's Magento security talk at Meet Magento DE 2026
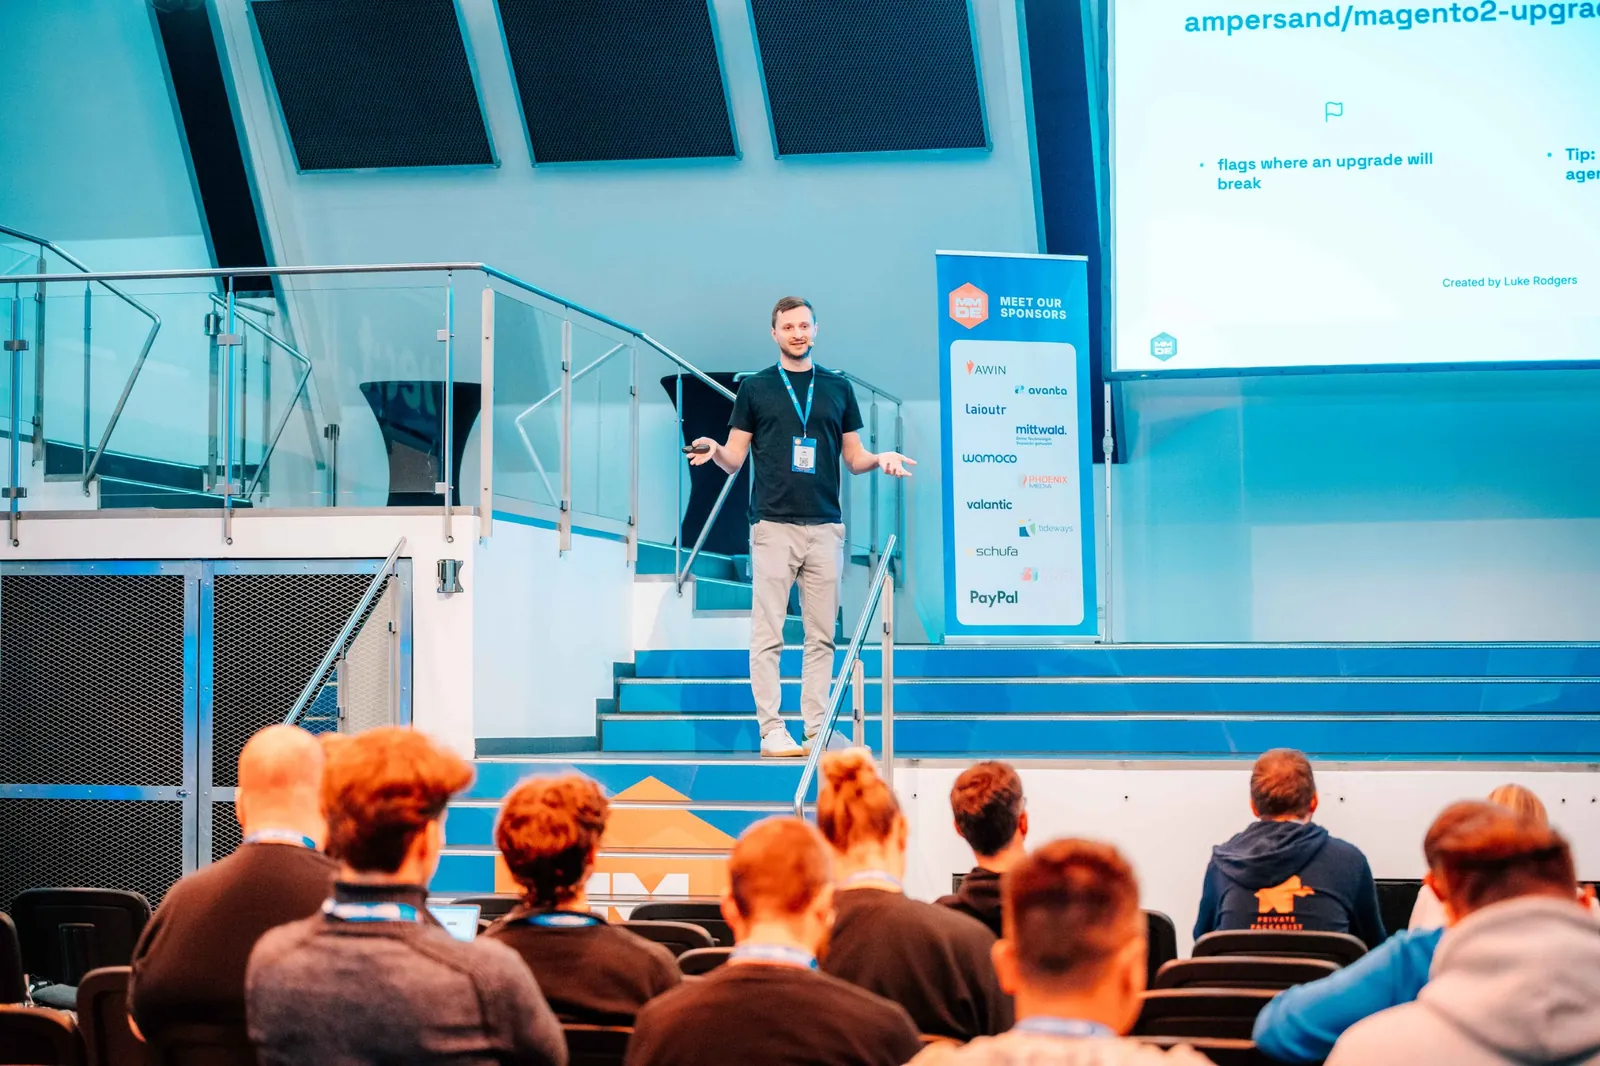
In October our Technical Commerce Lead Jiří Brada drove from Brno to Mainz for Meet Magento DE, where he gave a talk called The Priority We’re Getting Wrong. Jiří has spent almost ten years working in Magento, holds Adobe Commerce Expert and Master certifications, and built Package Maven, a public directory of Magento modules with tests.
The talk asks a blunt question: why do so many stores leave Magento security patches uninstalled for weeks after Adobe has released the fix?

Exploits now arrive in days, not weeks
Why unpatched Magento stores are a growing risk
The numbers are uncomfortable. The gap between Adobe publishing a security patch and attackers having a working exploit has dropped from 63 days, to 5 days, to minutes with the use of AI, because anyone can now read a patch and ask an AI model to build the attack. Yet a week after Adobe’s July security release, two in three of the tens of thousands of stores Jiří tracks still hadn’t applied it. Three months later, nearly one in five still hadn’t.
For a retailer, an unpatched store means someone else can read every order and customer record, inject malicious code into checkout and create their own admin account. Once you find a breach, you have 72 hours to report it to the regulator under GDPR, and the fines, compensation claims and brand damage follow.
Foundations, not heroics
How to make Magento patching boring
Jiří’s case is that the answer isn’t heroics. It’s making patching boring: a lean Magento install, custom code built properly, automated checks in the deployment pipeline, and a locked-down Composer setup so a compromised vendor can’t slip code into your build. He also covers virtual patching, where an edge rule blocks the exploit the same afternoon and buys time for the proper fix.
Jiří's verdict
Read the full Magento security slides
Jiří summed it up after the event: “We can do better. Let’s start with getting the foundations right.”
The full deck walks through the threat, where the Magento ecosystem stands today, and the practical defences, down to the exact Composer configuration changes. If you run a Magento or Adobe Commerce store, read it before your next patch day.

Find out how quickly you patch
Start with a conversation
Not sure how long it takes your store to get a security patch live? Get in touch and one of our lead developers will look at your setup and tell you what’s slowing it down. A Magento audit or Adobe Commerce audit will show where your codebase and server setup stand. If you’d rather hand patching over, see our Magento support and Adobe Commerce support services.